
AI Governance for Family Offices
Good AI governance names the people who can say yes, no, and stop, then gives staff rules they can follow in ordinary work.
What should an AI governance framework for a family office include?
Family office AI governance is the written answer to seven questions: Which tools are allowed? Which records may go in? Who gets access? Which vendors are trusted? What may automated agents do? What gets logged? How does the office recover or change providers?
Who Should Be Accountable for Family Office AI?
The family or its delegate sets the risk appetite. One executive approves uses and exceptions. Technology and security owners manage access and monitoring. Counsel reviews privacy, contracts, fiduciary duties, and jurisdiction. The person responsible for the underlying work still owns the result.
NIST organizes AI risk management around Govern, Map, Measure, and Manage. A family office can use that sequence without building a large committee. Keep the decision group small, write down who can stop a system, and name a backup for each critical role.
“Human in the loop” is not a job description
Name the person, the evidence they see, the decision they make, and the response when they are unavailable. A reviewer who receives a polished answer without its source records cannot provide a meaningful control.
Which Seven Decisions Belong in the Policy?
| Domain | Required decision | Evidence |
|---|---|---|
| Policy | Who approves uses, changes, and exceptions? | Roles and decision log |
| Data | Which records may enter each tool? | Classes, source register, retention |
| Access | Who can reach which records and functions? | Role matrix and access reviews |
| Vendors | Which providers are allowed under which terms? | Data-flow map, diligence, exit plan |
| Actions | What may software read, draft, recommend, or change? | Tool permissions and approval gates |
| Incidents | What is logged, escalated, contained, and reported? | Logs, contacts, exercise results |
| Continuity | How will the office recover or change providers? | Backups, export test, handoff record |
The private-wealth AI threat model supplies misuse cases. The build, buy, or steward framework assigns the long-term operating burden.
How Should the Rules Change With the Risk?
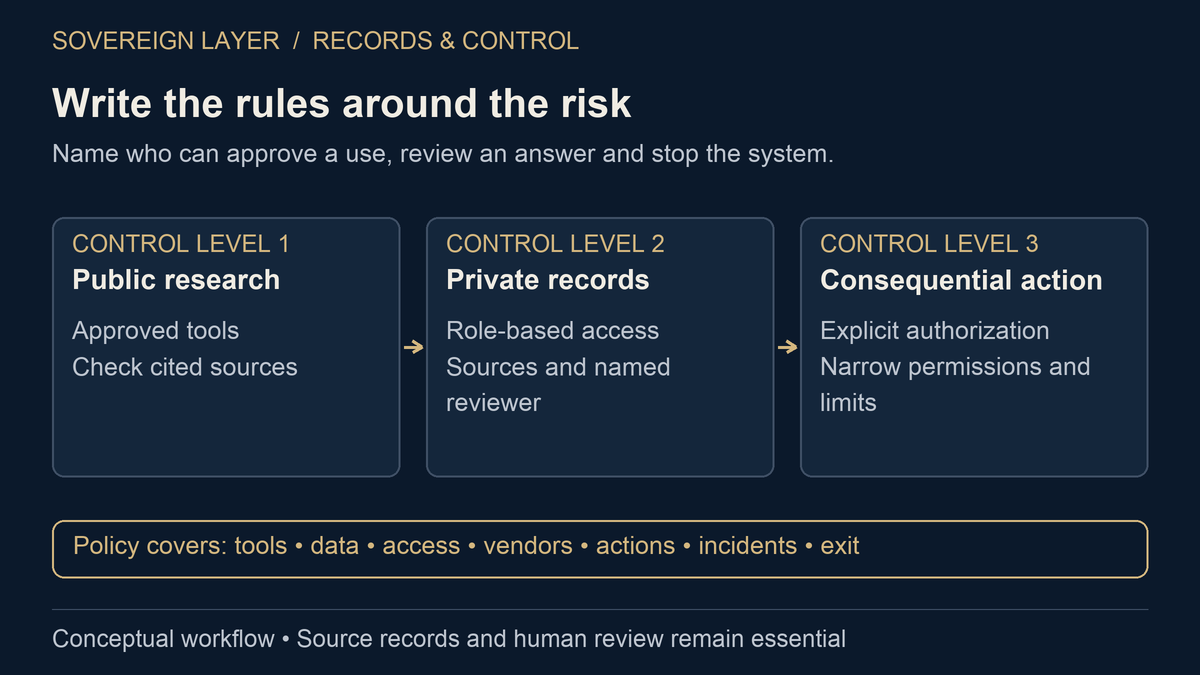
Public research may need an approved workspace, ordinary sign-in controls, and a source check. Searching agreements or preparing portfolio commentary calls for approved sources, role-based access, citations, stronger logs, and a named reviewer.
Money movement, permission changes, external messages, or changes to books and records require explicit authorization. Add dual control where it fits, narrow credentials, action limits, independent monitoring, and a tested way to contain or reverse mistakes.
Governance should also cover document systems already in use. SharePoint permissions can inherit through a site and can be interrupted at an item or library, so the office needs to understand actual access, not the intended folder structure. The same rule applies to connected AI tools: inspect the effective permission and the data crossing the boundary.
How Do You Turn Policy Into Working Rules?
- Inventory approved and unsanctioned AI tools, including AI features inside existing software.
- Choose one workflow and classify the records and possible harm.
- Assign an executive owner, technical owner, reviewer, and incident contact.
- Approve the model, data flow, retention, access, and vendor terms.
- Test ordinary work, misuse, prompt injection, missing sources, and incorrect outputs.
- Review access and performance when the model, connection, records, or use changes.
Write the first policy around a real task, such as the questions in the family office records guide. A policy written only in general terms will not tell an employee whether a capital-call notice, trust document, or adviser email belongs in a given system.
Track changes as decisions, not silent configuration updates. Record who approved a new model, connector, data source, or permission; what evidence they reviewed; when the decision expires; and how the office can reverse it. This makes later access reviews and succession work far easier.
Common questions
What belongs in a family office AI policy?
List allowed tools and uses, prohibited data, access rules, review steps, action limits, logs, vendor checks, incident contacts, exceptions, and the exit plan.
Should prompts and outputs be kept?
Keep them only as long as the work, legal duties, privacy needs, and audit trail require. Different workflows may need different retention rules.
How should outside advisers receive access?
Give each adviser a named account, a defined purpose, narrow permissions, an end date, and logged activity. Shared accounts are difficult to trace and revoke.
Sources and further reading
Sovereign Layer develops private AI for family offices. Will Scott designed the approach around firsthand investment experience and the need to keep private records under client control. Comparisons explain fit by task; they are not independent product rankings.
Book a Private Demo
Describe one workflow, the people involved, and the record types it uses. Please do not send sensitive files through the website.
Book a Private Demo